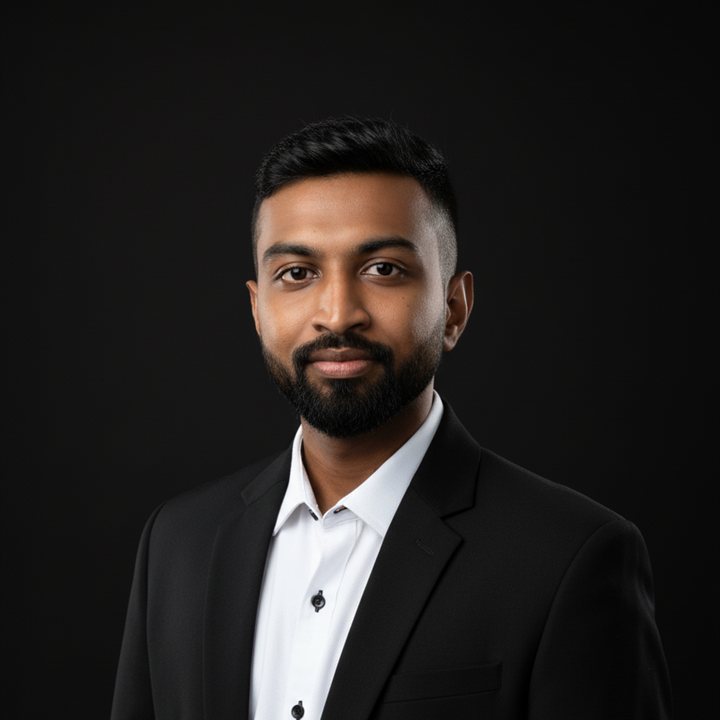
Hi, I'm
Induwara Nanayakkara.
Building and securing modern cloud, application, and software delivery environments through practical security engineering and DevSecOps.
Security designed as an embedded, frictionless discipline that strengthens every stage from the local editor to active runtime defense.
About me
I am a Engineer specializing in cloud security, application security, and DevSecOps, currently working at Innov8 Pvt Ltd.
My work centers on hands-on implementation of enterprise security solutions — from securing multi-cloud environments and workloads to embedding security controls into software development and CI/CD workflows.
Day to day, I perform application security assessments using SAST and DAST methodologies, implement and administer security platforms such as Veracode, Prisma Cloud, and Zimperium, and collaborate with development, infrastructure, and security teams to establish practical secure development practices.
"I care about security that enables delivery rather than blocking it. Pragmatic telemetry, shared developer responsibility, and verifiable posture over bureaucratic friction."
Before my current role, I worked in IT Risk and Security Operations at Allianz Insurance Lanka Limited, gaining invaluable experience within a highly regulated financial and insurance services environment.
Career timeline
Engineer – Cloud and AppSec
Innov8 Pvt Ltd · Sri Lanka
- check_circle Implement and manage DevSecOps and cloud security solutions across enterprise environments.
- check_circle Perform application security assessments using SAST and DAST methodologies.
- check_circle Implement and administer security platforms including Veracode, Prisma Cloud, and Zimperium.
- check_circle Secure cloud environments and workloads across Microsoft Azure and AWS.
- check_circle Integrate security controls and scanning tools into GitHub and CI/CD workflows.
- check_circle Monitor and improve cloud security posture management (CSPM) and vulnerability management processes.
- check_circle Conduct security validations and provide recommendations that improve application and cloud security posture.
- check_circle Collaborate with development, infrastructure, and security teams, automating security processes within pipelines.
IT Risk and Security Operations
Allianz Insurance Lanka Limited
Hands-on experience gained in IT Risk and Security Operations within a regulated insurance environment, maintaining compliance, investigating alerts, and executing continuous operational risk assessments.
What I work on
Security engineered as an active, integrated partner to modern product velocity, eliminating friction while elevating operational assurances.
Application Security
Finding and fixing weaknesses in software before attackers do — across source code, third-party open-source dependencies, APIs, and mobile applications.
Cloud Security
Building pervasive visibility and policy controls across multi-cloud environments so misconfigurations, IAM over-permissions, and drift are caught early.
DevSecOps
Shifting security left by embedding automated verification directly into delivery pipelines, turning manual security gates into fast developer self-service feedback.
Security Engineering
Hardening underlying infrastructure, orchestrating vulnerability remediation pipelines, and governing container baselines and Infrastructure-as-Code configurations.
How I approach security
A repeatable engineering lifecycle — security as a process, not a single tool.
Understand
Map assets, environments, and risk context before acting.
Assess
Evaluate posture through SAST, DAST, and cloud posture findings.
Design
Define practical controls that fit real delivery workflows.
Evaluate
Compare solutions against requirements through structured POCs.
Validate
Verify controls actually work using testing and validation tooling.
Implement
Integrate security into cloud platforms and CI/CD pipelines.
Improve
Monitor results and continuously raise the security baseline.
Where security applies
Hover a capability to highlight the layer it protects. Illustrative architectural model, structured for clarity.
Technology ecosystem
Professional platforms with confirmed hands-on production experience, alongside personal lab and research tooling.
Veracode
HANDS-ONSAST, DAST, and SCA analysis for identifying and remediating software risk.
Zimperium
HANDS-ONMobile threat defense and runtime protection for mobile applications.
Prisma Cloud
HANDS-ONCSPM and cloud workload protection across multi-cloud environments.
Wiz
HANDS-ONCloud-native application protection with deep posture and workload visibility.
Tenable
HANDS-ONExposure management and vulnerability assessment across infrastructure.
Pentera
HANDS-ONAutomated security validation testing controls against real attack techniques.
GitHub
HANDS-ONIntegrated security scanning and controls into GitHub-based CI/CD workflows.
Docker / Python
PERSONAL LABContainerizing utilities and scripting security automation integrations.
Security engagements
Generalized descriptions of professional engineering engagements. Customer identities, internal assets, and confidential details are intentionally omitted.
Limited visibility of misconfigurations and posture gaps across a large multi-cloud estate.
Onboarded cloud accounts onto a CSPM platform, defined posture policies, and established continuous compliance monitoring.
Hands-on platform implementation and administration, working alongside infrastructure teams to drive remediation.
Strengthened cloud security posture and an ongoing posture management practice for the enterprise environment.
Security needed to be embedded into the software development lifecycle without slowing delivery or adding friction.
Integrated code security scanning into GitHub-based CI/CD workflows with automated analysis and policy checks.
Built the integrations, triaged initial findings, and guided development teams through automated remediation.
Security scanning became a standard part of the delivery pipeline across enterprise delivery teams.
Production applications at a financial-sector organization needed runtime protection against active exploitation attempts.
Deployed and tuned RASP instrumentation together with the organization's core application and security teams.
Supported implementation, configuration, and validation of the runtime self-protection capability.
Runtime self-protection delivered for critical enterprise workloads in the financial sector.
BFSI organizations needed to evaluate application security solutions against real requirements before investing capital.
Scoped and executed proof-of-concept engagements with clearly defined, verifiable technical success criteria.
Led technical evaluations and demonstrated solution capabilities directly to security stakeholders and architects.
Successful POCs across multiple BFSI organizations supporting informed, defensible investment decisions.
Labs & experiments
Personal lab: independent learning projects, prototypes, and technical experiments. These are not professional client engagements or production enterprise systems.
OpenCode
Exploring AI-assisted coding agents and evaluating where they fit into secure developer workflows without introducing hallucinations or supply-chain flaws.
Ollama
Running local language models privately on host hardware to prototype air-gapped security triage, CVE summarization, and automation ideas.
Python Security Automation
Writing scripts and small tools that automate repetitive audit checks, query cloud vendor REST APIs, and export compliance artifacts.
Docker & DevSecOps Pipelines
Containerizing tools and assembling demo CI pipelines with integrated security scanning steps, image linting, and minimal attack surfaces.
Git & GitHub Workflows
Practicing protected branch policies, signed commit validation, pull request verification gates, and zero-trust repository hygiene.
BSc (Hons) Computer Networks and Security
Wrexham Glyndŵr University
Undergraduate degree focused on computer networks, network protocols, defensive systems, and security fundamentals.
Curriculum Vitae & Technical Record
A structured, print-ready summary of my experience, technical focus areas, and education. Open it and choose “Save as PDF” in your browser's print dialog.
Let's connect
The most reliable way to reach me is by email or LinkedIn. I am always open to discussing cloud security, application security, and DevSecOps engineering initiatives.